
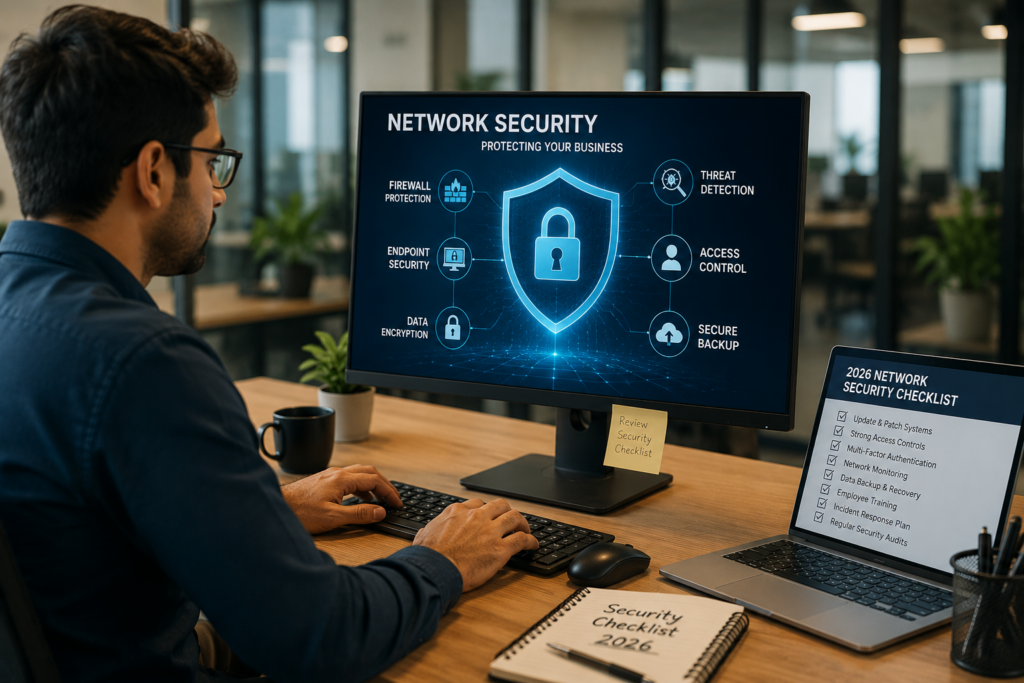
Cyber risk has stopped being an IT department problem in India and become a boardroom problem. The average cost of a data breach for an Indian organisation hit an all-time high of ₹25.5 crore in 2026, a jump of nearly 16% over the previous year, and AI-generated attacks now account for roughly a quarter of all malicious breaches. Indian organisations face thousands of attack attempts every week, and phishing, cloud misconfigurations, and supply-chain compromise remain the most common ways attackers get in.
For enterprises, the stakes are higher still. A single breach doesn’t just cost money – it can halt production lines, expose customer data protected under the Digital Personal Data Protection (DPDP) Act, and quietly erode the trust of clients and partners who assume your network is secure. The good news is that most breaches exploit gaps that a structured security review would catch. This checklist walks through the eleven areas every enterprise should audit heading into 2026, based on the deployments Electrocore Systems designs and manages for enterprise clients across India.
Table of Contents
Map and Segment Your Network
You cannot protect what you haven’t mapped. Start by inventorying every device, server, and endpoint connected to your network – including IoT devices, IP cameras, and VoIP handsets that are often forgotten in security audits. Once mapped, segment the network so that a breach in one zone (say, a guest Wi-Fi network) can’t spread to finance servers or core business applications. Enterprises are increasingly adopting Zero Trust architectures, where no device or user is trusted by default, and every access request is verified regardless of where it originates. Well-designed networking solutions build this segmentation in from day one rather than bolting it on after an incident.
Upgrade Firewalls and Intrusion Prevention
A perimeter firewall alone is no longer sufficient. Next-generation firewalls that combine deep packet inspection, intrusion prevention (IPS), and application-layer filtering give your network the ability to spot and block threats before they reach internal systems. For distributed enterprises, cloud-managed firewalls with centralized policy control make it possible to enforce the same security rules across every branch office without a dedicated engineer at each site.
Secure Your Wi-Fi and Wireless Access Points
Wireless networks are a favourite entry point for attackers because they’re easy to overlook. Every enterprise access point should run WPA3 encryption, use unique credentials per device or user, and sit on a segmented VLAN separate from core business systems. Guest and vendor Wi-Fi should never touch the same network as finance, HR, or operational technology. If your organisation spans multiple locations, this is worth revisiting alongside your broader network infrastructure planning, since inconsistent wireless security across sites is one of the most common audit findings.
Tighten Access Control, Physical and Digital
Network security and physical security are converging fast. Card readers, biometric access, and elevator access restrictions that once sat in a separate “facilities” budget are now part of the same conversation as firewalls and VPNs, because a stolen badge or an unmonitored server room door can undo months of digital hardening. Role-based access control — where employees only reach the systems and physical areas their job requires — should apply consistently across both domains. Electrocore’s access control solutions are typically deployed alongside network hardening projects for exactly this reason.
Integrate Surveillance with Network Monitoring
IP cameras and video management systems generate a constant stream of data across your network, and they’re also frequently targeted themselves — an unsecured camera feed is a well-documented attack vector. Enterprises should ensure surveillance infrastructure sits on its own segmented network, uses encrypted feeds, and is monitored with the same rigor as any other connected device. Beyond security, a properly integrated network camera and video management system doubles as an early-warning tool, helping security teams correlate physical anomalies (an after-hours entry) with network alerts (an unusual login) in real time.
Know About (Network Security)
Lock Down VoIP and Unified Communications
Voice and video systems are IP-based today, which means they inherit all the risks of any other network endpoint — plus a few of their own, like toll fraud and call interception. Every VoIP deployment should run on encrypted signalling and media (SRTP/TLS), sit behind a session border controller, and require multi-factor authentication for admin portals. This is a checklist item enterprises frequently skip because voice systems are viewed as “just phones” rather than networked infrastructure, but toll fraud alone costs businesses billions annually worldwide.
Patch, Update, and Retire Old Firmware
Unpatched routers, switches, and IoT firmware are among the easiest ways for attackers to gain a foothold, precisely because patching is unglamorous and easy to defer. Enterprises should maintain a patch management calendar, prioritise internet-facing devices, and set a hard retirement date for any hardware that’s no longer receiving security updates from its manufacturer. Automating this process – rather than relying on manual tracking across dozens of devices – significantly cuts the window of exposure.
Train Employees on Phishing and Social Engineering
Technology can only do so much when the attack targets a person rather than a system. Phishing, including voice phishing and SMS-based scams, remains the single most common way attackers gain initial access to Indian organisations. In 2026, this problem has gotten harder to spot: AI-generated deepfake voice and video calls are now being used to impersonate CEOs and CFOs to authorise fraudulent transfers, a scale of impersonation that traditional awareness training wasn’t built to catch. Regular, updated phishing simulations and a clear internal process for verifying unusual financial requests are now essential, not optional.
Build Compliance Into the Network, Not Around It
The DPDP Act has changed the calculus for Indian enterprises handling personal data. Breach notification obligations, data localisation considerations, and penalties for non-compliance mean that data protection can no longer be treated as a legal afterthought bolted onto a technical deployment. Network segmentation, encryption at rest and in transit, and detailed access logging all make compliance audits faster and breach notifications more precise when — not if — an incident occurs.
Establish (and Test) an Incident Response Plan
Even well-defended enterprises get breached; what separates a contained incident from a business-ending one is how fast the response happens. A documented incident response plan should specify who isolates affected systems, who notifies regulators under the DPDP Act, and who communicates with customers and partners – with the plan tested at least annually through a tabletop exercise. Organisations with a rehearsed response plan consistently report lower breach costs and faster recovery than those improvising in real time.
Partner with a Provider Who Sees the Whole Network
The single biggest checklist item is often the simplest: don’t try to manage all of this in isolation. Enterprise networks now span structured cabling, wireless, VoIP, video surveillance, and access control – and a vulnerability in any one of these can compromise the rest. Providers who design and manage the network holistically, the way Electrocore does for enterprises across hospitality, education, financial, and residential sectors, can catch the gaps that fall between siloed vendors and siloed teams. For a deeper look at how these pieces fit together, our post on network solutions for enterprise scalability covers the infrastructure side of this same conversation.
Conclusion
Enterprise network security in 2026 isn’t a single product or a one-time project — it’s an ongoing discipline that spans architecture, hardware, people, and policy. AI-powered threats, deepfake fraud, and a tightening compliance environment under the DPDP Act mean that the checklist above isn’t optional groundwork; it’s the minimum bar for doing business safely in India today. The enterprises that treat security as designed-in rather than bolted-on are consistently the ones that recover fastest when something does go wrong — and, more often, the ones that avoid the incident altogether.
If it’s been more than a year since your organisation ran through a checklist like this one, that’s a good sign it’s time. Electrocore Systems works with enterprises across Mangalore and beyond to design, deploy, and manage secure, scalable network infrastructure — from firewalls and structured cabling to access control and surveillance. Contact our team for a network security assessment, or browse more insights on our blog for practical guidance on building resilient business infrastructure.